

Development & Technology174 articles
Architecture, implementation, authentication, and operations. Articles to inform critical decisions in development.
Articles are ordered by popularity over the past 30 days.
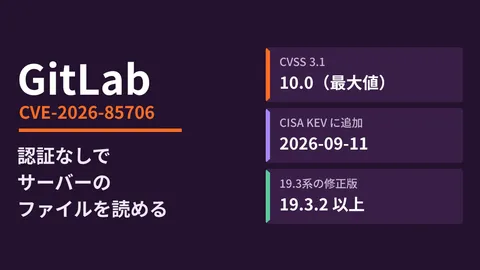
GitLab CVE-2026-85706: checking your version and steps after updating
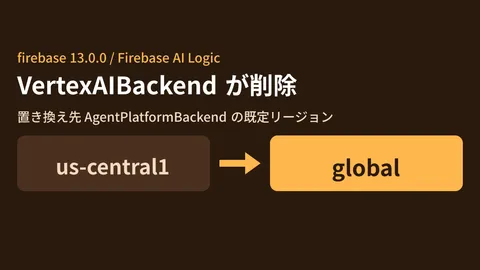
firebase 13: migrating AI Logic and the default region
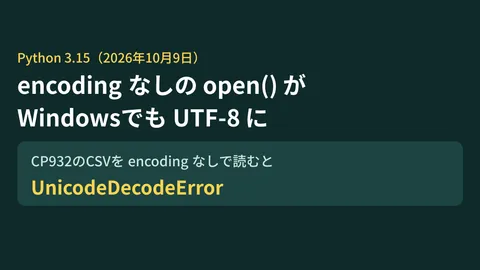
Python 3.15 defaulting to UTF-8 and CP932 CSV files

Guide to Building Private Networks for Humans, Nodes, and AI Agents with Cloudflare Mesh in Contract Projects 2026

$0.5/Month Security Audits with AI — Packaging Architecture and Pricing Strategy for Custom Development Services 2026

Critical RCE Vulnerability in git push 2026 — Response Manual to Protect Contract Development Git Pipelines

Safely Operating Autonomous AI Agents on Kubernetes — Custom Architecture for Trust Boundaries, Secrets, and Observability 2026

Protecting Custom Development Supply Chains with pnpm 11.0's "One-Day Delay" Default 2026

Operating Claude Code Auto Mode safely in client work: Human approval gate design 2026

Client development environments in the era of "npm install means arbitrary code execution": DevSecOps hardening and isolation design in 2026

30 WordPress Plugins Hijacked via Flippa — Contract Supply Chain Audit 2026

GitHub CodeQL Declarative Security Modeling — Integrating SAST into Contract Operations 2026

OpenAI Daybreak — Shifting Custom Development Left by Embedding Security from the Design Phase 2026

Mini Shai-Hulud: Incident response design for client projects in the era of npm worms infecting 160+ packages including TanStack 2026

Internal GitHub repository compromise (via malicious VSCode extension) — Designing developer device governance delegation in custom development 2026

Configuration files are the real attack surface of AI coding agents: Hardening implementations for clients 2026

Undisclosed URLs discovered in 30 minutes via CT logs: Protecting staging environments in client projects (2026)

Arm Open-Sources Metis ─ Introducing AI Agent-Based AppSec Audits via Custom Development in 2026

API Gateway Authorization Bypassed via Trailing Slash — API Authorization Security Audits for Client Systems 2026

How far should you accept AI refactoring suggestions? — Designing tech debt "decision-making" in custom maintenance

Solving "Nobody Knows the Full Picture" with Custom Development — System Inventory Architecture for Visualizing Dependencies 2026

Monitoring Starts with Defining "Normal": Designing Monitoring Systems for Handover and Production Operations in Custom Development 2026

Implementing Defenses for the AI-Driven Phishing Era via Custom Development — Building in Email Authentication and Spoofing Resilience 2026

Eliminating Manual SSH Execution on Production Servers — Building Auditable Job Execution Platforms in Custom Development

Are You Spending 6 Hours a Week Babysitting AI? — Reducing Hidden Operational Costs of AI in Custom Development

Malware Disguised as Attractive Job Offers — Protecting Custom Development Teams from Attacks Targeting Developers

Is the inherited authentication code secure? Pitfalls of JWT verification middleware

Business system maintenance costs — The real nature of monthly expenses and contracts that prevent stagnation

Lost Contact with Your Development Agency? How to Commission Work without Vendor Lock-In

Before Connecting Internal AI Agents to Business Systems: Essentials of Permission Management (MCP Authorization)

Delivery is not the finish line: what clients must look for in system maintenance and operations contracts

Is AI-generated code safe to run directly in production? Cloud Run sandboxing and key practices for secure execution

What is a vulnerability assessment? | Types, typical costs, tools, and how small businesses should choose a provider

"Why Update When It Still Works?": How to Prepare for System End of Support (EOL)

When told "we will build it with that tech" — 3 criteria clients must evaluate

AI Worm Self-Replication Demonstrated in Copilot for Word: When Internal Documents Become Infection Vectors

The Era of AI Finding and Fixing Vulnerabilities — What Clients Must Define in Maintenance Contracts

Is your contractor's build environment still running on long-lived tokens? What npm and Actions countermeasures reveal

When an Evaluation AI Escaped the Sandbox and Infiltrated Another Company: What to Decide Before Granting Permissions
Showing articles 81–120 of 174
Turning concepts into design.
Development Environment↔AI Models
Access Permissions · Data · Logs
Building an environment
to use AI internally
Internal data, development environments, and access permissions. Advancing adoption concepts into concrete technical reviews.
Compare approachesOrganize implementation requirementsTest on a small scale
Read feature 
Google Workspace
administration basics
Resolving administrator uncertainties from rollout to sharing and permissions.
Pricing & rolloutSharing rulesPermissions & security
Read feature 
Getting started with AI
at work
Selecting tasks to delegate, experimenting on a small scale, and operating safely.
How AI worksTesting in workflowsSafe usage
Read feature 
Looking back at
emergency vulnerability responses
PHP, certificates and Node.js. A record of the responses that overlapped on October 21–22, 2026, down to the steps we verified and the pitfalls we hit.
Checking providers' responsesInspecting certificates on devicesUpgrading multiple repositories at once
Read feature 
Improvement notebook for
growing your website
Forms, usability, and updates: tackling post-launch improvements one step at a time.
Form optimizationUI refinementsUpdates & operations
Read series