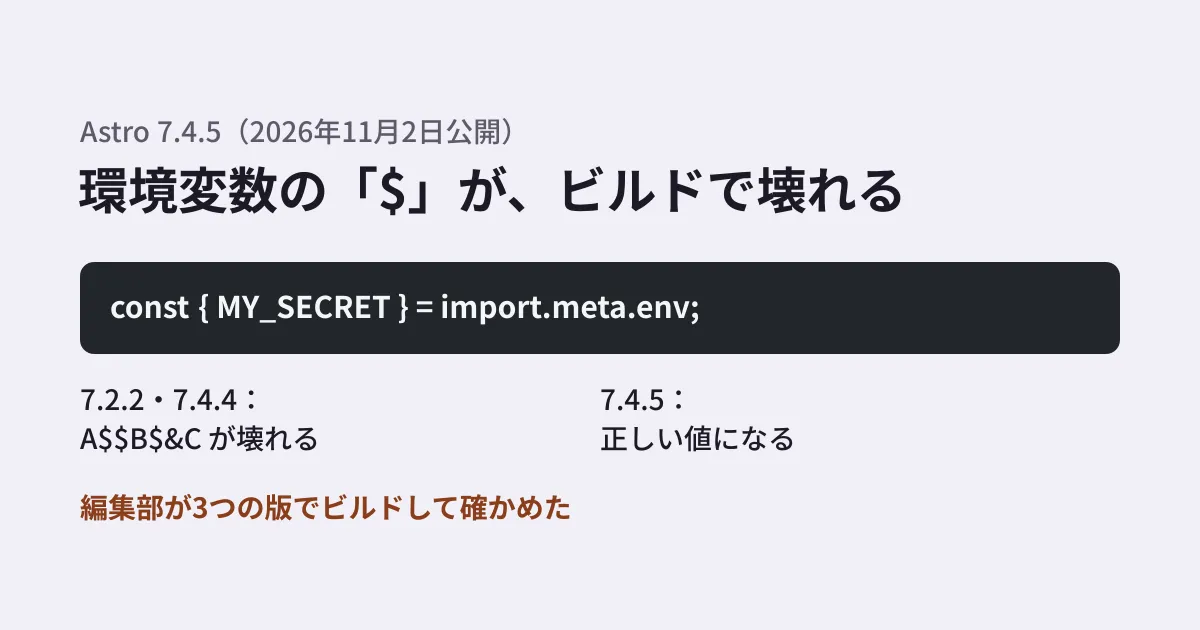
If an API key or password contained $, the value on an Astro site could change only in the result of astro build. If that value is used to authenticate with an external API, authentication would fail only in production. According to the bug report, the development server produces the correct value, so this is a bug where it is hard to notice that the cause lies in the value itself.
The changelog for Astro 7.4.5, published to npm on November 2, 2026, included a fix for this kind of bug. The editorial team built the same page on versions before and after the fix and confirmed that the value actually breaks and that 7.4.5 fixes it. As of November 6, 2026, the newer 7.4.6 and 7.4.7 have also been published.
The bug described in the changelog
The packages/astro/CHANGELOG.md in the Astro repository has the following entry for a fix in 7.4.5 (summary).
Fixed a bug where values containing
$sequences such as$$and$&were corrupted byastro buildwhen server-side code read theimport.meta.envobject directly (for example,const { MY_SECRET } = import.meta.env)
$$ and $& are sequences with special meaning in the replacement string of JavaScript's String.prototype.replace. $$ is replaced with a single $ character, and $& is replaced with the matched string itself. When this special meaning takes effect in processing that is supposed to embed the value as is, the value changes.
According to the pull request for the fix (#18559), the cause was passing the value to String.prototype.replaceAll as a string, and this was changed to passing a function (the meaning of the replacement string in replaceAll is the same as in replace). The pull request and the reporting issue (#18557) also list forms that put it into a variable, such as const env = import.meta.env, as affected. For values containing $` or $', it is reported that instead of the value changing, the build fails with PARSE_ERROR (the editorial team has not verified these two).
Building on three versions to confirm it
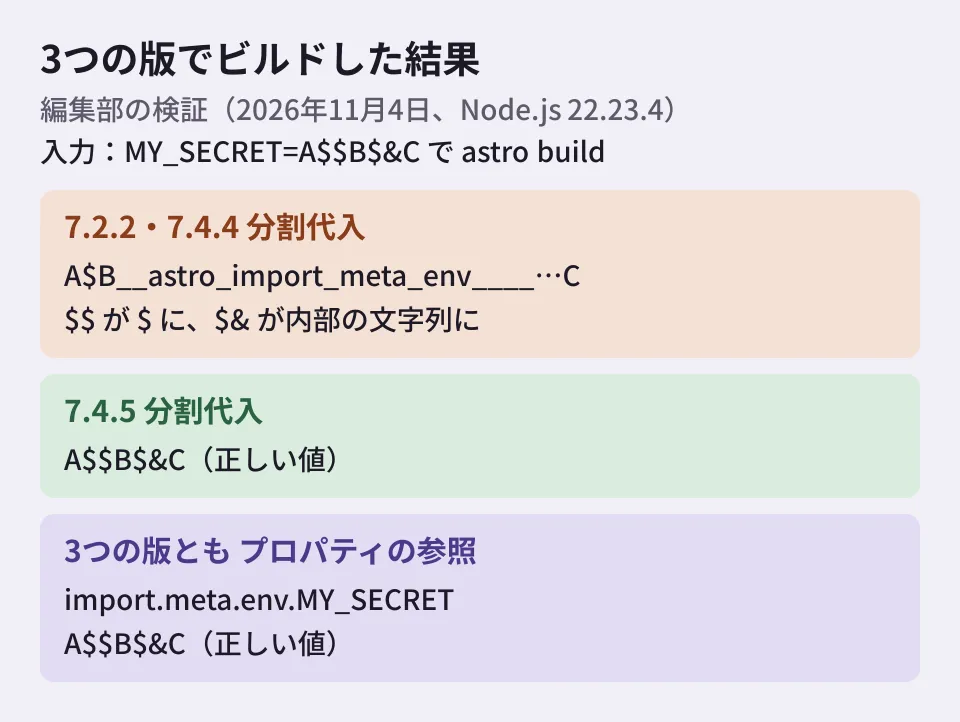
We compared three versions under the same conditions.
- Environment: Linux in a cloud work environment, Node.js 22.23.4
- Versions: Astro 7.2.2 (an example from the 7.2 series), 7.4.4 (the version right before the fix), 7.4.5 (the version with the fix)
- Input: set the environment variable
MY_SECRETtoA$$B$&Cand runastro build - Page: output the same value in two ways, by destructuring and by property access
---
const { MY_SECRET } = import.meta.env;   // 分割代入
const direct = import.meta.env.MY_SECRET; // プロパティの参照
---
<p id="destructured">{MY_SECRET}</p>
<p id="direct">{direct}</p>
The built dist/index.html output is as follows (with the HTML escape & converted back to &).
| Release | Destructuring | Property access |
|---|---|---|
| 7.2.2 | A$B__astro_import_meta_env_____…_____C (corrupted) | A$$B$&C |
| 7.4.4 | A$B__astro_import_meta_env_____…_____C (corrupted) | A$$B$&C |
| 7.4.5 | A$$B$&C | A$$B$&C |
With destructuring, $$ became the single character $, and an internal string starting with __astro_import_meta_env appeared in the position of $&. This is the special replacement sequences taking effect as is. Property access (import.meta.env.MY_SECRET) produced the correct value on all three versions. In 7.4.5, destructuring also produced the correct value.
We also noticed something during verification. On 7.2.2, when the value was written as ab$$cd$&ef in a .env file, it became ab$$&ef even with property access, and the $cd part disappeared. According to the Vite documentation, .env values are expanded as variables by dotenv-expand, and to include $ in a value you escape it with \ (Astro's environment variable loading uses Vite's loadEnv). To separate the effect of how .env is written from this bug, the results in the table were obtained by passing the value through an environment variable. If you write a value containing $ in .env, escape it and then check the value in the build output (the editorial team has not verified the results with escaping).
Checking the impact on your own site
The affected code is code that reads import.meta.env as an object. In the Astro source, forms where import.meta.env is not followed by . are what this processing targets. You can find places matching the same condition with the following grep. It finds destructuring, spread, const env = import.meta.env, import.meta.env[key], and passing to functions.
grep -rnE 'import\.meta\.env([^.A-Za-z0-9_$]|$)' srcWhen we checked this site's source (src, excluding article bodies), there were four references to import.meta.env, all of them property accesses like import.meta.env.PROD. The grep above had 0 matches, so this site is not affected by this bug. However, destructuring is a form you would naturally choose when reading multiple values together, and the changelog example also uses this form. For sites whose production was outsourced, you cannot know whether they are affected until you check the code.
Here is the order for checking.
- Use the grep above to find places that read it as an object
- If you find any, check whether the values of the environment variables in use contain
$(do not display the values themselves on screen or in logs) - Upgrade to 7.4.5 or later (the latest as of November 6, 2026 is 7.4.7). If you cannot upgrade right away, rewrite it in the form
import.meta.env.KEY
Other changes in 7.4.5
7.4.5 also includes three other fixes (as stated in the changelog; not verified by the editorial team).
- Paths containing invalid percent-encoding (for example,
/%C0%AFor a lone%) were logged asInvalid URL encodingerrors and routed without being decoded. They now return400 - String tag names in
.astrodynamic tags, JSX, and MDX are handled more strictly. Only the valid element name portion is output, and/or=can no longer alter the markup. Strings that do not start with an element name ('!--'or an empty string) produce an error - A bug where running
astro dev statusor similar from a sandbox or as another user deleted the lock file of a running development or preview server
With the second one, code that builds tag names from external data may produce errors after upgrading. It is safest to check where dynamic tags are used before upgrading.
7.4.6 and 7.4.7 were published on November 5, 2026. 7.4.6 contains fixes for items such as i18n fallback and the astro check exit code, and 7.4.7 contains a fix for the image endpoint (as stated in the changelog). We confirmed that this fix remains in the 7.4.7 source, but we have not verified builds on these two versions.
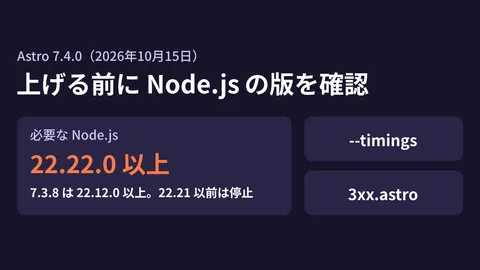
If upgrading from the 7.2 series, also note that the minimum Node.js version was raised to 22.23.4 in 7.4.2 (as stated in the changelog). If you only rewrite the code and stay on an old version, other advisories remain. For example, versions below 7.2.8 have GHSA-26w7-cxv4-gfx2 (remote code execution through optimization of untrusted AVIF images), and versions below 7.3.2 have GHSA-98hj-9722-w3j8 (XSS in script and style elements in JSX and MDX). We cover pinning the Node.js version in build environments in our article on the Node.js version in Cloudflare Workers Builds, and the changes in 7.4 in our article on Astro 7.4.
Scope of verification
On November 4 and November 6, 2026, we retrieved the CHANGELOG in the Astro repository (packages/astro/CHANGELOG.md) and checked the entries for 7.4.5 through 7.4.7. We checked the publication date of 7.4.5 (November 2, 2026) and the latest version on the npm registry, and the meanings of
$$and$&inreplacein the MDN repository (mdn/content). On November 6, we also checked issue #18557, pull request #18559, the 7.4.7 source, the GitHub advisories, and the Vite documentation. Verification was done on November 4, 2026, in the editorial team's working directory, by placing the same page on the three versions Astro 7.2.2, 7.4.4, and 7.4.5 and running a static build (once per version). We have not verified server-rendered configurations (configurations using an adapter), forms usingastro:env, behavior on the development server, or builds on 7.4.6 and 7.4.7.
For maintenance of sites built with Astro and how to upgrade versions, please consult us through website production and renewal consultation.
References
- astro/packages/astro/CHANGELOG.md(withastro/astro)
- astro(npm)
- Build corrupts import.meta.env values containing $ when a file reads the env object(issue #18557)
- Fix build corruption of import.meta.env values containing $(PR #18559)
- GHSA-26w7-cxv4-gfx2 (Astro advisory)
- GHSA-98hj-9722-w3j8 (Astro advisory)
- Env Variables and Modes(Vite)
- String.prototype.replace()(MDN)