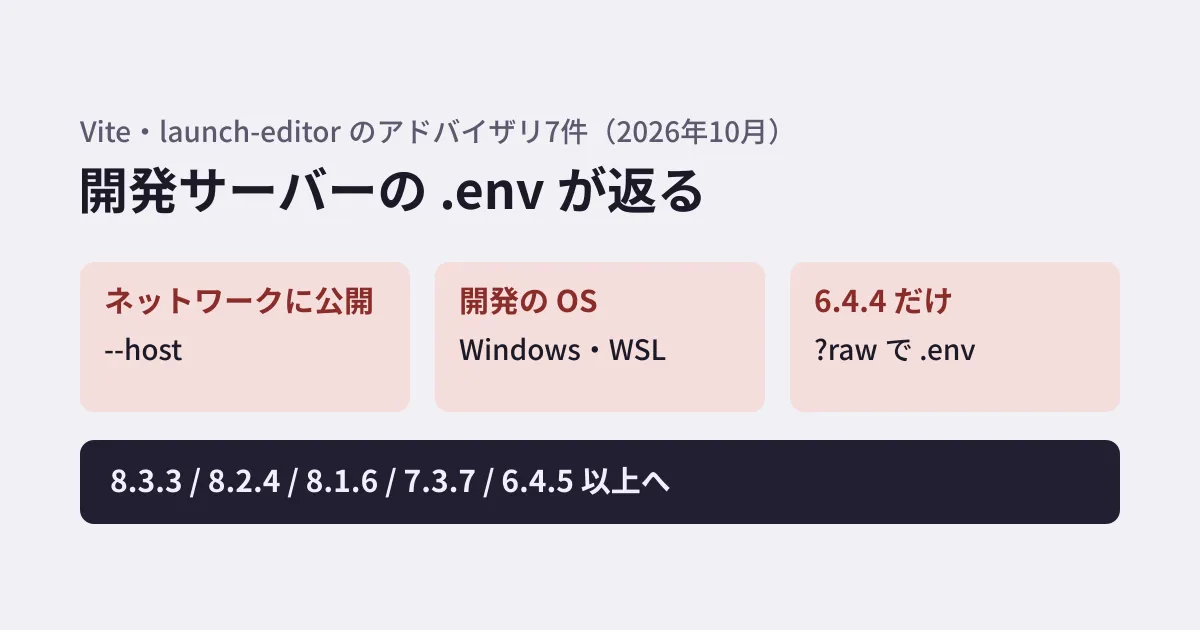
Exposing the dev server on the internal network with npm run dev -- --host to check the display on a physical smartphone. Running the dev server as-is on a staging server to show designers or clients. Both are ways of exposing the dev server to the network through Vite's --host setting.
Between October 20 and 29, 2026, a total of seven advisories were registered in the GitHub Advisory Database for this Vite dev server and for launch-editor, the component that opens an editor from the browser. Three of them, in Vite, state that "when the dev server is exposed to the network," the contents (or part of the contents) of files that should never be served, such as .env containing API keys, may be returned.
Astro, Nuxt and SvelteKit depend on Vite, and some React projects also use Vite for development. This article sorts out the conditions under which each of the seven advisories applies and shows the results of running versions before and after the fixes locally.
The seven advisories and when they apply
All seven concern the dev server (vite / vite dev) and its surrounding components, and the conditions in the advisories relate to how the dev server is started, exposed and used with middleware.
| Advisory | Severity | What can happen | Main conditions |
|---|---|---|---|
| GHSA-rq7h-c2jc-7f22 | MODERATE | Files outside server.fs.allow are returned | Exposed via --host etc., not Windows, importing a file whose path has the same form as an absolute host path |
| GHSA-vfpm-58rq-9qcg | MODERATE | ?vite-wasm-instance returns the first 4 bytes of a file | Exposed via --host etc., running on Node.js or Deno (8.2 and 8.3 lines) |
| GHSA-8g5g-mxqh-grgj | MODERATE | Adding ?raw or similar returns files covered by server.fs.deny (.env etc.) | Exposed via --host etc. (6.4.4 only) |
| GHSA-9jrq-w75r-8gcw | LOW | A malicious site can run scripts in the dev server's pages | Passing the browser URL directly to transformIndexHtml in middlewareMode: true or appType: 'custom' |
| GHSA-r825-w8mm-5pxw | MODERATE | The editor interprets arguments as options, and commands may be executed | Using WSL, Vim, Emacs, etc., and an attacker can create a file whose name starts with + - |
| GHSA-698v-4r3x-3vcv | MODERATE | % is not handled on Windows, and commands may be executed | Windows, an attacker can place a file with a crafted name, etc. |
| GHSA-587h-7wmj-h5pm | HIGH | Removes the need to "place a file" from the condition above | Windows |
The first three all require that "the dev server is exposed to the network with --host or server.host." Vite's server.host defaults to 'localhost', and adding --host or setting 0.0.0.0 or true makes it listen on LAN and public addresses as well.
The last three are issues in launch-editor, and Vite is affected because it uses this component. For teams with anyone developing on Windows or WSL, these need checking even if the dev server is not exposed to the network.
Fixed version
Every release line has a fixed version. Except for 6.4.5, they were published to npm on October 6, and the advisories were registered afterward. Newer versions of each line were also released on November 9. As of November 11, no advisory lists those versions as fixed versions. If you upgrade, the easiest approach is to move to the latest version of your release line.
| Release line | Fixed version (this version or later) | Latest in the release line (as of November 11) |
|---|---|---|
| 8.3 | 8.3.3 | 8.3.7 |
| 8.2 | 8.2.4 | 8.2.6 |
| 8.0・8.1 | 8.1.6 | 8.1.7 |
| 7 | 7.3.7 | 7.3.8 |
| 6 | 6.4.5 (6.4.4 is affected by GHSA-8g5g) | 6.4.6 |
Vite+ (vite-plus on npm), a toolchain that includes Vite, is also listed as affected by six of the advisories (all except GHSA-8g5g) and is fixed in 1.1.0.
The 6.x line needs attention. 6.4.4 was the October 6 fixed version, but part of the fix had not been backported, so queries such as ?raw could bypass server.fs.deny. This is GHSA-8g5g from October 29, and it is fixed in 6.4.5.
Astro 7.4.10 specifies vite: ^8.3.6 as a dependency, and @nuxt/vite-builder in Nuxt 4.6.4 specifies ^8.3.5 (per the npm registry as of November 11, 2026). Upgrading the framework to a newer version also brings Vite to a fixed version or later, but a lockfile can keep an older version pinned, so check the actual version with the following steps.
What we found in local testing
In our editorial test environment (Linux, Node.js v22.23.4), we installed Vite 8.3.2, 8.3.3, 6.4.4 and 6.4.5 one version at a time, placed a dummy .env (SECRET_KEY=abc123), started the dev server and sent requests with curl. We did not expose it to the network and tested on localhost only.
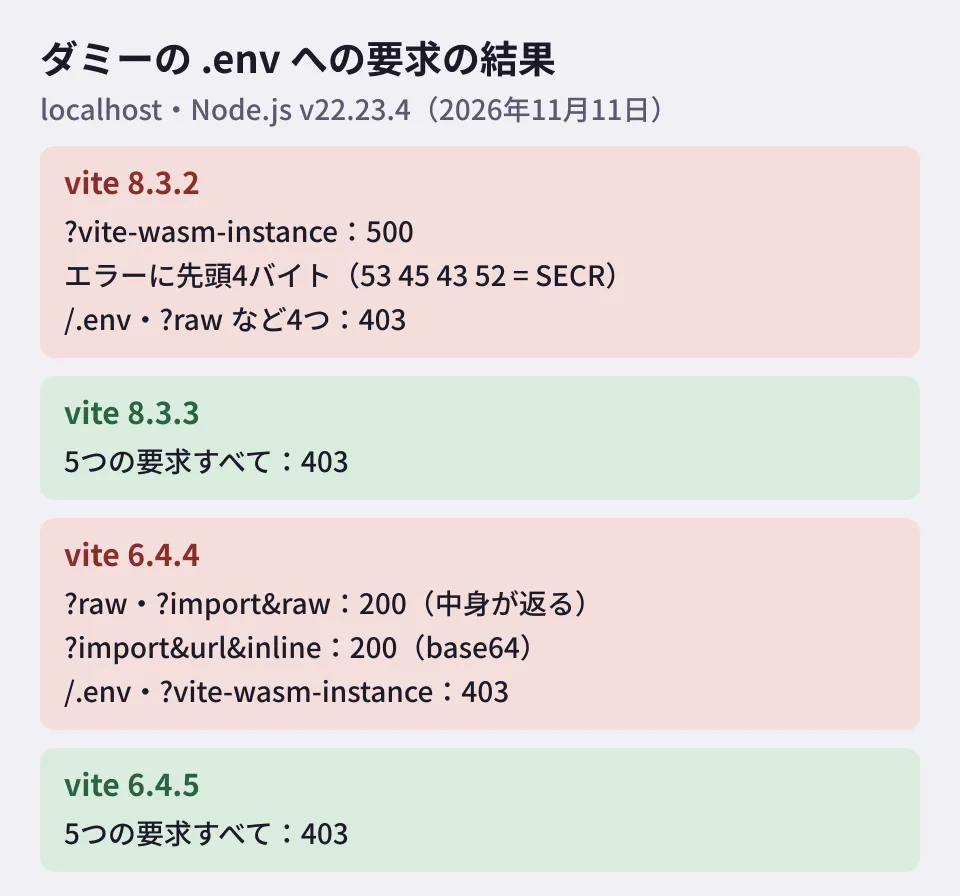
- 8.3.2:
/.env?vite-wasm-instancereturned 500, and the error body and the server log showed "expected magic word 00 61 73 6d, found 53 45 43 52." 53 45 43 52 reads as "SECR" in text, which is the first 4 bytes of.env. - 6.4.4:
/.env?rawand/.env?import&rawreturnedexport default "SECRET_KEY=abc123\n"with status 200, and/.env?import&url&inlinereturned the contents encoded in base64./.envitself returned 403. - 8.3.3 and 6.4.5: all five requests we tried returned 403.
Because this was tested on localhost, it does not show that "an attack succeeds over the network." However, if the dev server is exposed, the same requests can also arrive from other devices on the internal network. We did not reproduce the three launch-editor issues on Windows or WSL, or the middlewareMode issue.
Steps to check and update (editorial suggestion)
From here on are the editorial team's suggestions.
1. Check the versions actually installed. Run the following in your project directory and compare the results with the fixed-version table above. Vite installed inside your framework is also shown.
npm ls vite2. Upgrade. If you use a framework, upgrade the framework and check again with npm ls vite. If you use Vite directly, upgrade to the fixed version of your release line or later.
3. Decide when the dev server may be exposed. Add --host only when needed, such as for testing on physical devices, and do not add it permanently to the dev script in package.json. If you show work to clients on a staging server, a rule of serving the output of vite build instead of the dev server makes you less exposed to dev server issues like these.
4. If you set server.fs.deny yourself, review it. On November 5, Vite's documentation added the note "This setting replaces the default list. Include any default patterns you want to keep in your own list." The default list consists of .env, .env.*, certificate and key file extensions, .npmrc, .yarnrc.yml, and anything inside .git. Also, this list does not apply to the public directory, so do not put secrets there.
We covered how to check for vulnerabilities on the framework side in our article on the October Next.js advisories. For how Astro handles environment variables, our article on Astro 7.4.5 is also useful.
Scope of verification
On November 11, 2026, we reviewed the seven advisories in the GitHub Advisory Database (web pages and API), the tags and CHANGELOG of vitejs/vite and the v8.3.7 documentation (including the public pages on vite.dev), and the publication dates and framework dependencies in the npm registry (desk research). As of November 11, no Vite advisories had been registered after October 29. We also started Vite 8.3.2, 8.3.3, 6.4.4 and 6.4.5 on localhost and compared the results of five kinds of requests for a dummy
.env(hands-on testing on Linux with Node.js v22.23.4; the steps and output are saved in the article's evidence record).
GleamHub's development, AI and automation consultations cover updating dependencies for sites under development and creating operating rules for development and staging environments. The approach depends on your setup, so please reach out via Contact us.
References
- GitHub Advisory Database — GHSA-8g5g-mxqh-grgj(Vite: server.fs.deny bypassed with queries)
- GitHub Advisory Database — GHSA-rq7h-c2jc-7f22
- GitHub Advisory Database — GHSA-vfpm-58rq-9qcg
- GitHub Advisory Database — GHSA-9jrq-w75r-8gcw
- GitHub Advisory Database — GHSA-587h-7wmj-h5pm(launch-editor)
- GitHub Advisory Database — GHSA-698v-4r3x-3vcv(launch-editor)
- GitHub Advisory Database — GHSA-r825-w8mm-5pxw(launch-editor)
- Vite — Server Options
- vitejs/vite — docs/config/server-options.md(v8.3.7)