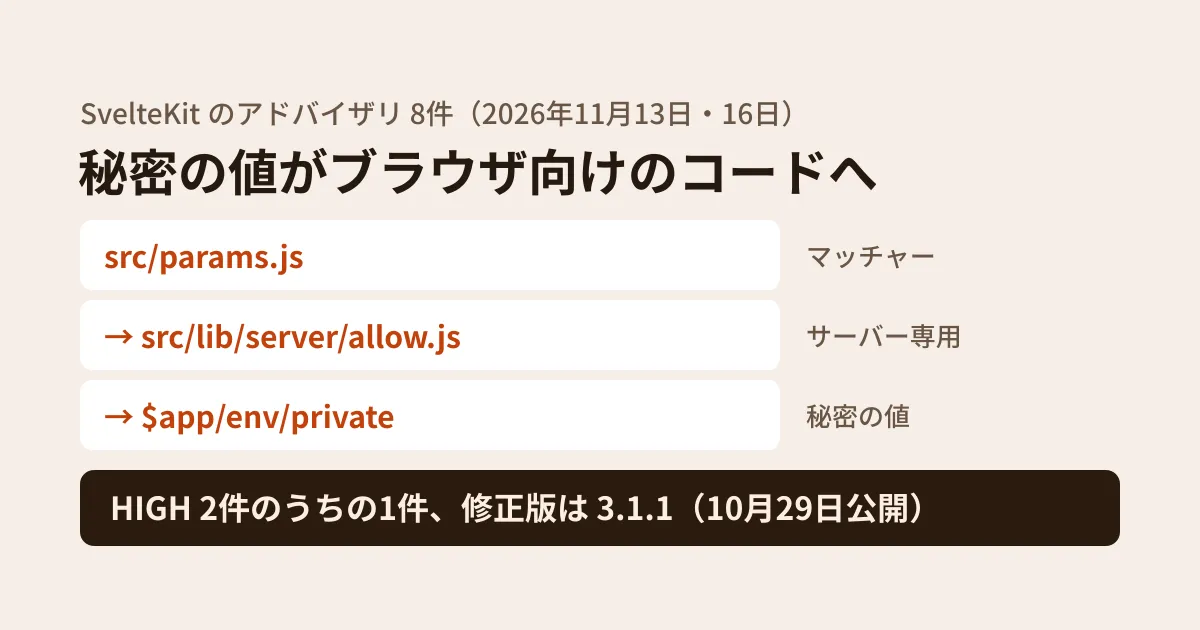
On sites built with SvelteKit, values such as API keys and database connection details are placed in "server-only" modules so that browser-bound code cannot import them. SvelteKit checks this separation at build time and stops with an error if the browser side tries to import them.
The advisory registered on November 16, 2026 (GHSA-m9j8-jcmv-hp69, severity HIGH) says this check does not work for imports made via src/params.js, so secret values can end up in browser-bound code. In the same week, a total of eight advisories were registered for SvelteKit itself and its official adapters (adapter-node, adapter-cloudflare, adapter-vercel and adapter-static).
Many of the eight apply only if you use experimental features or specific adapters. This article sorts out which advisories apply to sites with which settings, and presents the fixed versions and the order in which to check.
When the eight advisories apply
The publication date is the date of registration in the GitHub Advisory Database. Fixed versions are based on what the advisories state.
| Advisory (severity) | What can happen | Conditions for being affected | Fixed version |
|---|---|---|---|
| GHSA-m9j8-jcmv-hp69(HIGH) | Server-only values end up in browser-bound code | On 3.0.0–3.1.0, importing server-only modules from src/params.js | kit 3.1.1 |
| GHSA-3r8g-jcqq-3p5j(HIGH) | A crafted request blocks the event loop for a long time | Experimental remote functions are enabled and form, query or command is used (2.42.0 and later) | kit 3.1.1 |
| GHSA-rqp5-r3wg-vg35(MODERATE) | A client-side navigation to a crafted link loads and runs code from another domain | It has router.resolution: 'server' configured | kit 3.1.1/2.70.4 |
| GHSA-6cf5-gc4q-fm3x(MODERATE) | Arguments of separate query.batch calls get mixed up | Remote functions are enabled and a query.batch that is not exported is used (2.60.1 and later) | kit 3.1.1 |
| GHSA-mw6w-2fmv-pvw3(MODERATE) | The adapter-node server crashes | reroute rewrites paths with invalid percent-encoding into valid paths | kit 3.1.1/2.70.4 |
| GHSA-rqw3-x7hx-mm3p(MODERATE) | The adapter-node server crashes | With adapter-node (5.5.7 and later), returning some requests proxied through fetch (described in the CHANGELOG as text/event-stream responses) | adapter-node 6.0.1/5.5.8 |
| GHSA-5wg4-q3ww-283h(MODERATE) | Unintended rules get into _redirects | With adapter-cloudflare, external input can get into the links crawled during prerendering | adapter-cloudflare 8.0.2/7.2.10 |
| GHSA-jf9x-2fg2-hx4w(MODERATE) | Paths are treated as regular expressions in Vercel's routing configuration | With adapter-vercel or adapter-static, external input can get into the links crawled during prerendering | adapter-vercel 7.0.2/6.3.5、adapter-static 4.0.1/3.0.11 |
Remote functions are an experimental feature, which the advisories also describe as the "experimental remote functions flag." If you have not enabled them in your configuration, GHSA-3r8g and GHSA-6cf5 do not apply. Likewise, if you have not set router.resolution to 'server', GHSA-rqp5 does not apply.
The HIGH issue: importing server-only modules from params.js
In SvelteKit 3, the functions that check URL parameters (parameter matchers) are written together in src/params.js. The test app added in the fix commit (ae07803) is structured as follows.
// src/params.js
import { defineParams } from '@sveltejs/kit/params';

export const params = defineParams({
  gate: async (param) => {
    const { is_allowed } = await import('./lib/server/allow.js');
    return is_allowed(param) ? param : undefined;
  }
});
// src/lib/server/allow.js
import { SHOULD_EXPLODE } from '$app/env/private';
export function is_allowed(value) {
return value === SHOULD_EXPLODE;
}Files under src/lib/server/ and $app/env/private are places that browser-bound code is not supposed to be able to import. Before the fix, however, the build check did not count src/params.js as an "entry point that runs in the browser." The fix commit adds src/params.js as an entry point, along with the comment "param matchers run in the browser when router.resolution is 'client'."
The advisory explains that this import happens only when it goes through src/params.js. If your parameter matchers check allowed values against a secret list or verify them against a database, they need to be checked.
We have not verified this issue by building with versions before and after the fix and comparing whether values end up in the browser-bound output. The structure above is quoted from the test app in the fix commit, and a test was added so that the same structure causes a build error in the fixed version.
Fixed versions and release timing
The versions containing the fixes were published to npm before the advisories were registered.
@sveltejs/kit3.1.1: October 29, 2026. 2.70.4 in the 2.x line on November 5@sveltejs/adapter-node6.0.1: October 29 (5.5.8 in the 5.x line on November 5)@sveltejs/adapter-cloudflare8.0.2: October 29 (7.2.10 on November 5)@sveltejs/adapter-vercel7.0.2 and@sveltejs/adapter-static4.0.1: October 29 (6.3.5 and 3.0.11 on November 5)
As of November 20, the latest versions on npm are kit 3.4.0, adapter-node 6.0.5, adapter-cloudflare 9.0.0, adapter-vercel 7.0.5 and adapter-static 4.0.1. As of November 20, the GitHub Advisory Database contains no SvelteKit advisories registered after November 16.
adapter-cloudflare 9.0.0 (November 18) is a major version, and its CHANGELOG lists breaking changes, starting with "breaking: remove Cloudflare Pages support" and including the removal of the fallback option. Since the fix for GHSA-5wg4 is included in 8.0.2, our editorial recommendation is that sites running on Cloudflare Pages first upgrade to the latest 8.x release (8.0.3) and treat the migration to 9.0.0 as a separate task.
Sites still on the 2.x line need to be careful. A 2.x fixed version (2.70.4) is listed only for GHSA-rqp5 and GHSA-mw6w. For the two remote-function advisories (GHSA-3r8g affects 2.42.0 and later, GHSA-6cf5 affects 2.60.1 and later), only 3.1.1 is listed as the fixed version, and there is no fixed version in the 2.x line. If you have remote functions enabled on 2.x, you need to decide whether to upgrade to 3.x or stop using remote functions. GHSA-m9j8 is an issue with src/params.js (the style used from 3.0.0 onward), and the affected versions also start at 3.0.0.
Order for checking your own site (editorial suggestion)
From here on is our editorial suggestion. Applying the conditions in the table above in the following order lets you narrow things down quickly.
1. Check which versions you have installed.
npm ls @sveltejs/kit @sveltejs/adapter-node @sveltejs/adapter-cloudflare @sveltejs/adapter-vercel @sveltejs/adapter-static2. Check the imports in src/params.js. If you are on 3.x and have src/params.js, follow the import statements in it (including await import()) and see whether it imports files from the $app/env/private, $app/server, *.server.js or /server/ directories. If it does, upgrade to 3.1.1 or later and check whether the build passes; if it does not, rewrite the matchers so they do not use server-only values. If you published files built before the upgrade, also consider rotating any values (API keys and so on) that may have been included in those files.
3. Check your configuration. Look at the remote functions setting (experimental.remoteFunctions) and the value of router.resolution. In SvelteKit 3 the configuration is passed to sveltekit() in vite.config.js, while in 2.x it is under kit in svelte.config.js. If you use neither, the three advisories in the table (GHSA-3r8g, GHSA-6cf5 and GHSA-rqp5) do not apply.
4. Check each adapter. If you use prerendering with adapter-cloudflare, adapter-vercel or adapter-static and build links from external input such as CMS articles or user posts, open the generated _redirects or Vercel configuration once after upgrading and check for unintended rules.
We covered behavior changes when upgrading to SvelteKit 3.0 in our article on SvelteKit 3.0, and a Vite dev server issue from the same period in our article on the Vite vulnerability.
Scope of verification
On November 17, 2026, we reviewed the eight advisories in the GitHub Advisory Database (data from github/advisory-database), the sveltejs/kit repository (fix commit ae07803 and its test app, and the CHANGELOGs for kit, adapter-node and adapter-cloudflare), and the publication dates on the npm registry (desk research). On November 20, we rechecked that the advisories had not changed, that no new SvelteKit advisories had been published since, and the latest versions on npm and each package's CHANGELOG. We did not build with versions before and after the fixes or reproduce the issues by sending requests to a server.
GleamHub's development, AI and automation consulting can help with updating dependencies and reviewing builds for sites in development or in operation. Because the approach depends on your setup, please reach out via our contact form.
References
- GitHub Advisory Database — GHSA-m9j8-jcmv-hp69
- GitHub Advisory Database — GHSA-3r8g-jcqq-3p5j
- GitHub Advisory Database — GHSA-rqp5-r3wg-vg35
- GitHub Advisory Database — GHSA-6cf5-gc4q-fm3x
- GitHub Advisory Database — GHSA-mw6w-2fmv-pvw3
- GitHub Advisory Database — GHSA-rqw3-x7hx-mm3p
- GitHub Advisory Database — GHSA-5wg4-q3ww-283h
- GitHub Advisory Database — GHSA-jf9x-2fg2-hx4w
- sveltejs/kit — fix: prevent server-only modules from being imported into browser code via src/params.js(ae07803)
- sveltejs/kit — packages/kit/CHANGELOG.md
- sveltejs/kit — packages/adapter-cloudflare/CHANGELOG.md