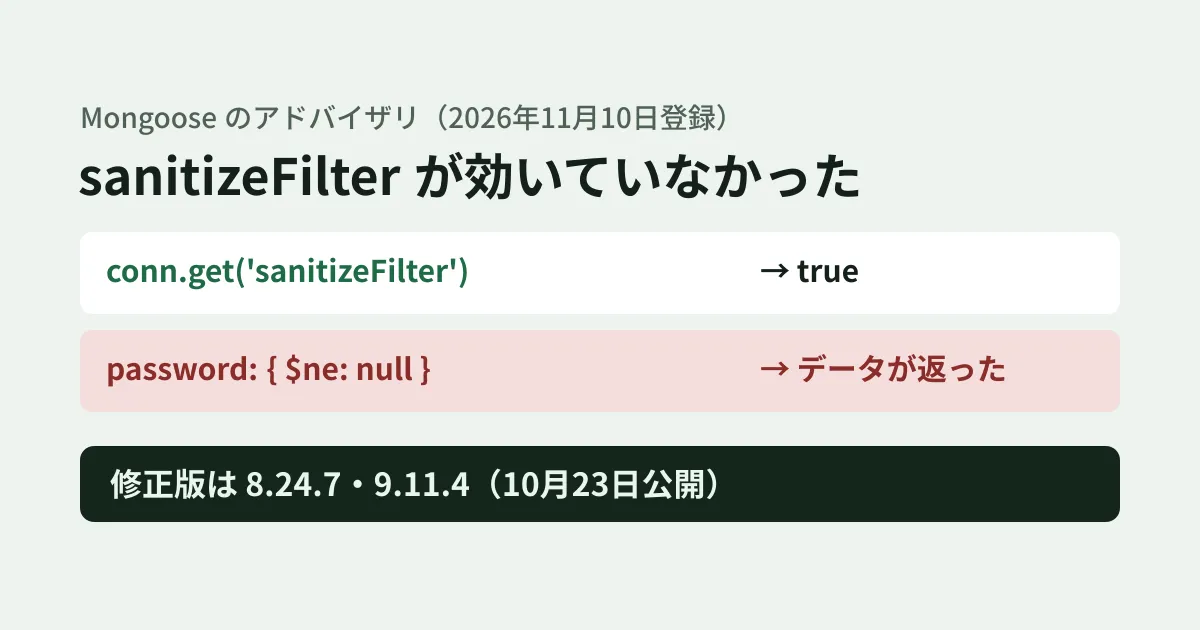
If JSON like {"username":"victim","password":{"$ne":null}} is sent to a login screen, the password condition becomes "anything that is not null", and the user's data is returned without knowing the password. To prevent this well-known attack on MongoDB applications (query selector injection), Mongoose has a setting called sanitizeFilter.
On November 10 (UTC), five Mongoose advisories were registered in the GitHub Advisory Database (they were published in the Mongoose repository on November 2). Of the three rated High or Critical, two concern cases where this sanitizeFilter was not taking effect even when enabled. Fixed versions are already available for both, the earliest released in August. This article covers when these three issues apply, the results of reproducing them on MongoDB 8.0 by version, and which versions to upgrade to.
The three high-severity issues
| ID (severity) | Details | Fixed version (8.x / 9.x) |
|---|---|---|
| GHSA-gg4r-jv3p-qx3c(High) | When enabled per connection, such as with createConnection(uri, { sanitizeFilter: true }), the setting reports true but is not applied to queries | 8.24.7 / 9.11.4 (released October 23) |
| GHSA-pcrw-h46h-c93h(Critical) | sanitizeFilter is not applied to countDocuments() only | 8.24.3 / 9.9.2 (released August 10) |
| GHSA-8332-j7wj-wjw4(High) | Loading, set() and update merging write to inherited properties such as toString, which can halt processing for the whole process | 8.24.7 / 9.11.4 (released October 23) |
Fixed versions are also available for 6.x and 7.x.
- The first and third: 6.13.12 and 7.8.13 (released October 23)
- The second: 6.13.11 and 7.8.12 (released August 10)
The remaining two registered the same day (both Moderate) are as follows. Their fixed versions are the same as for the first and third, and this article did not reproduce them.
- GHSA-6972-9mcm-vhwj: Passing a name containing
__proto__or similar toSchema.prototype.virtual()allowsObject.prototypeto be overwritten. This affects designs where user input determines schema field names (dynamic schemas, form builders and so on) - GHSA-wr5m-5jph-8m96: Putting a value such as
'constructor'in the discriminator key (__tby default) bypasses schema casting. If it is saved as is viaskipValidation: trueofbulkWrite()or similar, queries that return that data fail from then on
According to the first advisory, the per-connection setting has been out of step since Mongoose 6.0.0, when it moved to its current storage method. Setting mongoose.set('sanitizeFilter', true) for the whole app or specifying it per query is not affected.
The third is a problem where a user-submitted value such as { "toString": { "call": 1 } } overwrites Object.prototype.toString.call. The advisory states that "after the overwrite, every query, including those on unrelated models, fails with TypeError: _toString.call is not a function until the process restarts." It also lists a path through non-strict (strict: false) subdocuments that can bypass the schema's required validation.
Reproducing them on MongoDB 8.0 by version
On November 16, 2026, we started MongoDB 8.0.38 (official image mongo:8.0) in Docker in a Linux test environment. We ran the same script with Mongoose 8.24.2, 8.24.6, 8.24.7, 9.9.1, 9.11.3 and 9.12.1 installed from npm (Node.js 22.23.4). The only data was a single test record (username: 'victim', password: 'correct-password').
When sanitizeFilter takes effect, { $ne: null } is wrapped in $eq, fails to cast to the string field, and stops with CastError. When it does not take effect, the matching data is returned without knowing the password.
| What we tried | 8.24.2・9.9.1 | 8.24.6・9.11.3 | 8.24.7・9.12.1 |
|---|---|---|---|
Enabled per connection, { $ne: null } passed to findOne | Data returned | Data returned | Stopped with CastError |
Enabled globally, { $ne: null } passed to countDocuments | Counted as 1 | Stopped with CastError | Stopped with CastError |
Data containing toString: { call: 1 } passed to hydrate() | Later queries throw TypeError | Later queries throw TypeError | No effect |
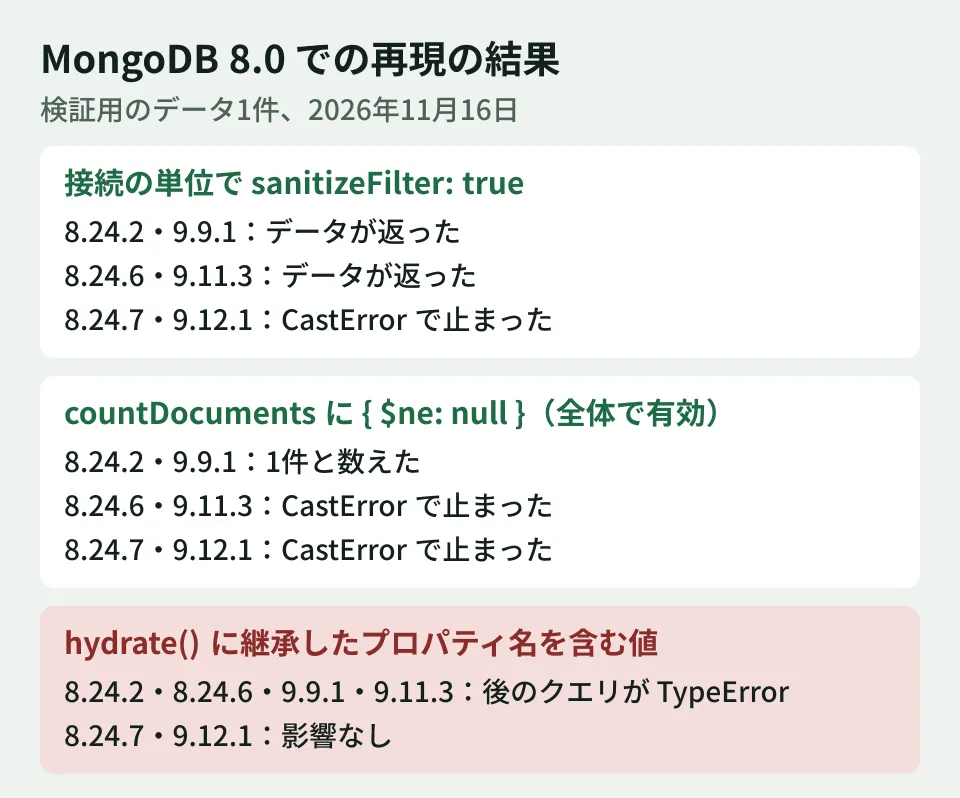
In the per-connection case, conn.get('sanitizeFilter') returned true even in versions before the fix. Simply checking the setting will not reveal that it is not taking effect.
In the toString case, simply passing data containing this value to Model.hydrate() caused query building to keep failing for later queries in the same process. Because this happens even when just loading data already saved to the database, if problematic data has already been saved, versions before the fix may stop every time it is loaded, even after restarting the app (we did not verify behavior after a restart).
Which version to upgrade to and what to check
From here on are the editorial team's suggestions.
- Upgrade to the latest version of your release line. On November 16 (UTC), 9.12.2, 8.24.10, 7.8.14 and 6.13.13 were released. As of November 20, these are the latest in each line. The changelog (CHANGELOG.md) includes a fix that changes
sanitizeFilterto cover all top-level keys starting with$. It says this is to prevent bypasses using MongoDB internal expressions such as$_internalSchemaXor. As of November 20, we found no advisory corresponding to this fix. Because these versions are newer than the fixed versions for the five advisories and also include this fix, upgrade to them. Usenpm ls mongooseto also check whether a different version is pulled in through a library. - Find where you set it per connection. If
sanitizeFilterappears in the arguments tocreateConnection(ormongoose.connect(, review your login and search processing on the assumption that it was not taking effect in versions before the fix. Until you upgrade, applying it to the whole app withmongoose.set('sanitizeFilter', true)worked within the scope of our tests. - Check value types at the entry point.
sanitizeFilteris the last line of defense. If you validate that the loginpasswordis a string when the request is received, you are not dependent on the Mongoose version. - Check logs from the period before the fix. If the third issue's overwrite occurred, there should be
_toString.call is not a functionerrors. Search your error monitoring and logs for this message.
Care is needed if you use Payload CMS's MongoDB adapter. @payloadcms/db-mongodb pins its mongoose dependency to a specific version rather than a range. 3.93.0, released November 4, pins it to 8.24.1, which falls within the affected range of all three issues. When installed in a test environment, npm ls mongoose showed only 8.24.1. In 3.94.0, released November 17, the pinned version changed to 8.24.7, which is within the fixed range for the five advisories. However, it does not include the November 16 sanitizeFilter fix described above (8.24.10). Because Payload builds its own query conditions, we did not verify which issues apply when used through Payload. You can upgrade with npm's overrides, but compatibility with Payload has not been confirmed.
We covered the November Node.js updates in our article on Node.js security updates. How to think about waiting periods when automating dependency updates is summarized in our article on Dependabot's default waiting period.
Scope of verification
On November 16, 2026, we reviewed the JSON for three advisories in github/advisory-database (GHSA-gg4r-jv3p-qx3c, GHSA-pcrw-h46h-c93h, GHSA-8332-j7wj-wjw4) and the npm publication dates (document research). We also ran reproduction scripts with Mongoose 8.24.2, 8.24.6, 8.24.7, 9.9.1, 9.11.3 and 9.12.1 against MongoDB 8.0.38 started in Docker in a Linux test environment (Node.js 22.23.4). On November 20, we rechecked, via the GitHub API, the five advisories registered the same day, Mongoose's CHANGELOG.md, the latest version of each line on npm, and the dependencies of
@payloadcms/db-mongodb3.94.0. We did not verify the 6.x and 7.x lines, paths viaset()or update merging, the path that bypasses validation throughstrict: falsesubdocuments, behavior after a restart, the two Moderate issues, or the effect of the November 16sanitizeFilterfix. For Payload CMS, we only installed@payloadcms/db-mongodb3.93.0 and checked its dependencies.
GleamHub offers development, AI and automation consultations on updating business systems that use MongoDB and reviewing login processing. What needs checking depends on your setup, so please reach out through our contact form.
References
- GitHub Advisory Database — GHSA-gg4r-jv3p-qx3c(Connection-level sanitizeFilter not applied)
- GitHub Advisory Database — GHSA-pcrw-h46h-c93h(sanitizeFilter not applied on countDocuments)
- GitHub Advisory Database — GHSA-8332-j7wj-wjw4(inherited properties when hydrating, setting, and merging)
- GitHub Advisory Database — GHSA-6972-9mcm-vhwj(Prototype pollution via Schema.prototype.virtual())
- GitHub Advisory Database — GHSA-wr5m-5jph-8m96(Discriminator key values matching inherited properties)
- Automattic/mongoose — CHANGELOG.md
- npm — mongoose
- npm — @payloadcms/db-mongodb