To reduce sales emails and automated submissions arriving through contact forms, some sites use a mechanism like ALTCHA, which has the browser perform a computation, instead of a CAPTCHA that asks users to select images. It is less work for users, but if the server-side verification is not working correctly, the form lets everything through.
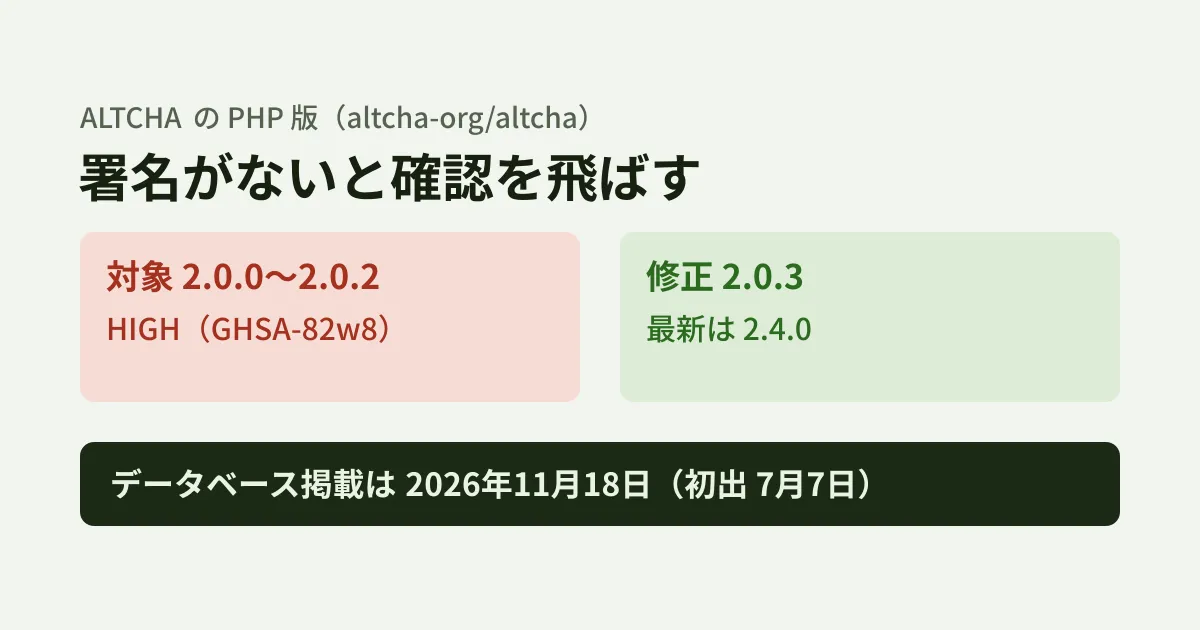
On November 18, 2026, an advisory (GHSA-82w8-65qw-gch6, CVE-2026-71481, HIGH) for a weakness that causes server-side verification to be skipped entirely in ALTCHA's PHP library (the Composer package altcha-org/altcha) was added to GitHub's advisory database. The same advisory had already been published in the ALTCHA repository on July 7. The fixed version, 2.0.3, was released on July 2, but sites that pin their Composer dependencies and have not updated remain affected. In this article, we use the advisory and the fix commits to outline the affected configurations and what to check.
Consequence
In ALTCHA, the server creates a challenge, attaches an HMAC signature using a secret key, and passes it to the browser. The browser finds the answer through computation and submits the challenge and answer together with the form. Using verifySolution(), the server checks whether the challenge's signature is one it issued and whether the answer is correct.
According to the advisory, verifySolution() in the 2.0 line skipped signature verification when a submitted challenge had no signature field (signature), even if hmacSignatureSecret was set. The pre-fix code used the following condition, so if the signature was null, it never entered the verification step.
// 2.0.2 まで(src/Altcha.php)
if (null !== $payload->challenge->signature && null !== $this->hmacSignatureSecret) {
    // 署名の確認
}
As a result, an attacker can pass verification simply by creating and solving a low-difficulty challenge of their own and submitting it with the signature field removed. The advisory describes the impact as "complete CAPTCHA bypass on every deployment that configures hmacSignatureSecret (the configuration recommended for production)."
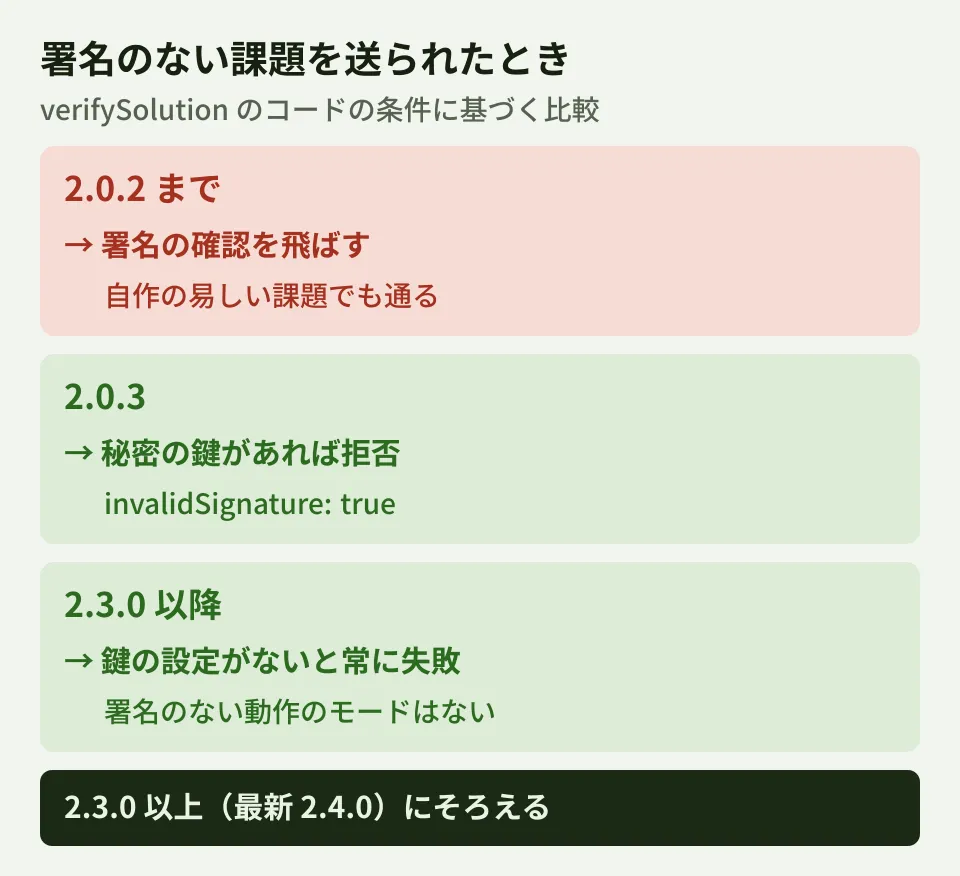
Affected versions and fixes
| Release | Published date | Handling of unsigned challenges |
|---|---|---|
| 2.0.0〜2.0.2 | April 7 – April 29, 2026 | Skips signature verification (affected) |
| 2.0.3 | July 2, 2026 | Rejected if a secret key is set (invalidSignature: true) |
| 2.3.0 | October 4, 2026 | Unsigned challenges never pass. Without a secret key configured, no challenge passes (breaking change) |
| 2.4.0 | November 17, 2026 | Latest. Keeps the 2.3.0 behavior |
The 2.0.3 fix (commit 8b02ad2, "reject missing challenge signature when secret is set") makes the function return verified: false when a secret key is set and the signature is missing. A test was also added to confirm that challenges with the signature removed do not pass. In addition, commit 6f94721 in 2.3.0 explains in a code comment that "as in the JavaScript version, there is no unsigned mode of operation. Neither unsigned challenges nor verification without a signing key will ever pass."
In the database advisory, affected versions are 2.0.0 or later and earlier than 2.0.3. The advisory in the ALTCHA repository, however, lists affected versions as "2.0.0 or later and earlier than 2.0.2" and the fixed version as 2.0.3, so the two disagree on 2.0.2. Because the code at the 2.0.2 tag still contains the pre-fix condition, this article treats 2.0.2 as affected. The 1.x line (latest is 1.3.3 from April 2) is not included as affected in either advisory.
What to check on the form side (editorial suggestion)
- Check the installed version. Check the version with
composer show altcha-org/altcha. If it is 2.0.0–2.0.2, upgrade withcomposer require altcha-org/altcha:^2.4or similar. If you sharecomposer.lock, deploy the updated lock file as well. - Before upgrading, read about breaking changes in the intermediate versions. ALTCHA's policy is to ship breaking changes even in updates that change only the second number, such as 2.3.0 or 2.4.0 (2.4.0 release notes). According to the release notes, 2.2.0 rejects challenges with
keySignaturecreated before the update, and in 2.3.0 verification always fails unless you pass a secret key (hmacSignatureSecret). 2.4.0 included changes such as no longer retrying 4xx responses in verification that uses the external verification service (Sentinel). Confirm that form submissions work in a test environment before releasing to production. - Pass the secret key on every verifying server. 2.0.3 fixes this weakness, but in 2.0.3–2.2.0, signature verification itself is not performed if no secret key is configured. In 2.3.0 and later, that configuration gap surfaces as "all submissions rejected" rather than letting everything through. To guard against configuration gaps as well, standardize on 2.3.0 or later, and first confirm that every server performing verification is passing the key.
- Check that you use the verification result correctly. Confirm that submissions are accepted only when
verifiedin the return value ofverifySolution()istrue, and that processing stops otherwise. Code that lets submissions through on exceptions or errors remains a hole even after upgrading. - Check libraries for other languages and plugins separately. This advisory covers the PHP version. For ALTCHA libraries in other languages and CMS plugins, check with each distributor which version they use internally.
We covered design for the problem of sales emails piling up through contact forms in our article on form design, and changes to Google reCAPTCHA scoring in our article on reCAPTCHA. Spam protection mechanisms should be treated as part of maintenance, including updates after they are installed.
Scope of verification
On November 19, 2026, we checked the JSON for GHSA-82w8-65qw-gch6 (published November 18, 2026) in github/advisory-database, the diffs of commits 8b02ad2 (2.0.3, July 2, 2026) and 6f94721 (2.3.0, October 4) in altcha-org/altcha-lib-php, tags v2.0.0–v2.4.0, and the publication dates of each version on Packagist (document research). On November 20, we rechecked the altcha-org/altcha-lib-php advisory (published July 7, 2026, retrieved via the GitHub API), the
verifySolution()code at tags v2.0.2–v2.4.0, and the release notes for v2.0.3–v2.4.0. No version newer than 2.4.0 has been released. We have not reproduced the bypass. We have not checked the versions used by ALTCHA libraries for other languages or by CMS plugins.
GleamHub's website development consultations cover reviewing spam protection for contact forms and setting up site maintenance. Please reach out through our contact form.
References
- GHSA-82w8-65qw-gch6: ALTCHA PHP: verifySolution bypasses HMAC signature check when challenge signature is absent(github/advisory-database)
- altcha-org/altcha-lib-php — commit 8b02ad2(verifySolution - reject missing challenge signature when secret is set)
- altcha-org/altcha-lib-php — commit 6f94721(verifySolution rejects when no signature secret is configured)
- Packagist — altcha-org/altcha
- altcha-org/altcha-lib-php — Security Advisory GHSA-82w8-65qw-gch6
- altcha-org/altcha-lib-php — Releases (release notes for v2.0.3–v2.4.0)